Encryption protects your data on disk and on the network, but the moment a server starts working on it, it sits in memory in the clear.
Checked 18 November 2026. Confidential computing keeps data encrypted while it is being processed, by running the workload inside a hardware trusted execution environment (TEE) that the server's owner, host operating system and hypervisor can't read. The processor enforces it, and a signed attestation report lets you check it before you hand over any secrets. One caveat runs through all of it: someone still decides which software gets your keys, and that's usually the provider, so confidential computing shortens the list of people you have to trust to a few.
Contents
- How confidential computing works
- What is a trusted execution environment?
- How attestation works
- What each setup hides
- AMD SEV-SNP vs Intel TDX
- Confidential AI
- What confidential computing doesn't protect
- When confidential computing is worth it
- What confidential compute means on Hippius
- Which providers offer confidential computing
- Common questions about confidential computing
How confidential computing works
Data lives in three states. At rest, it sits on a disk, and disk encryption protects it. In transit, it moves across a network, and TLS protects it. In use, it sits in memory while a processor works on it, and on an ordinary server nothing protects it there. Whoever controls the machine, through the host operating system, the hypervisor or physical access, can in principle read it.
The Confidential Computing Consortium, a Linux Foundation group whose members include the major chip makers and clouds, defines the field as protecting data in use by performing computation in a hardware-based, attested trusted execution environment. Its own description of the gap is that data is usually encrypted at rest and in transit, but not while in use in memory.
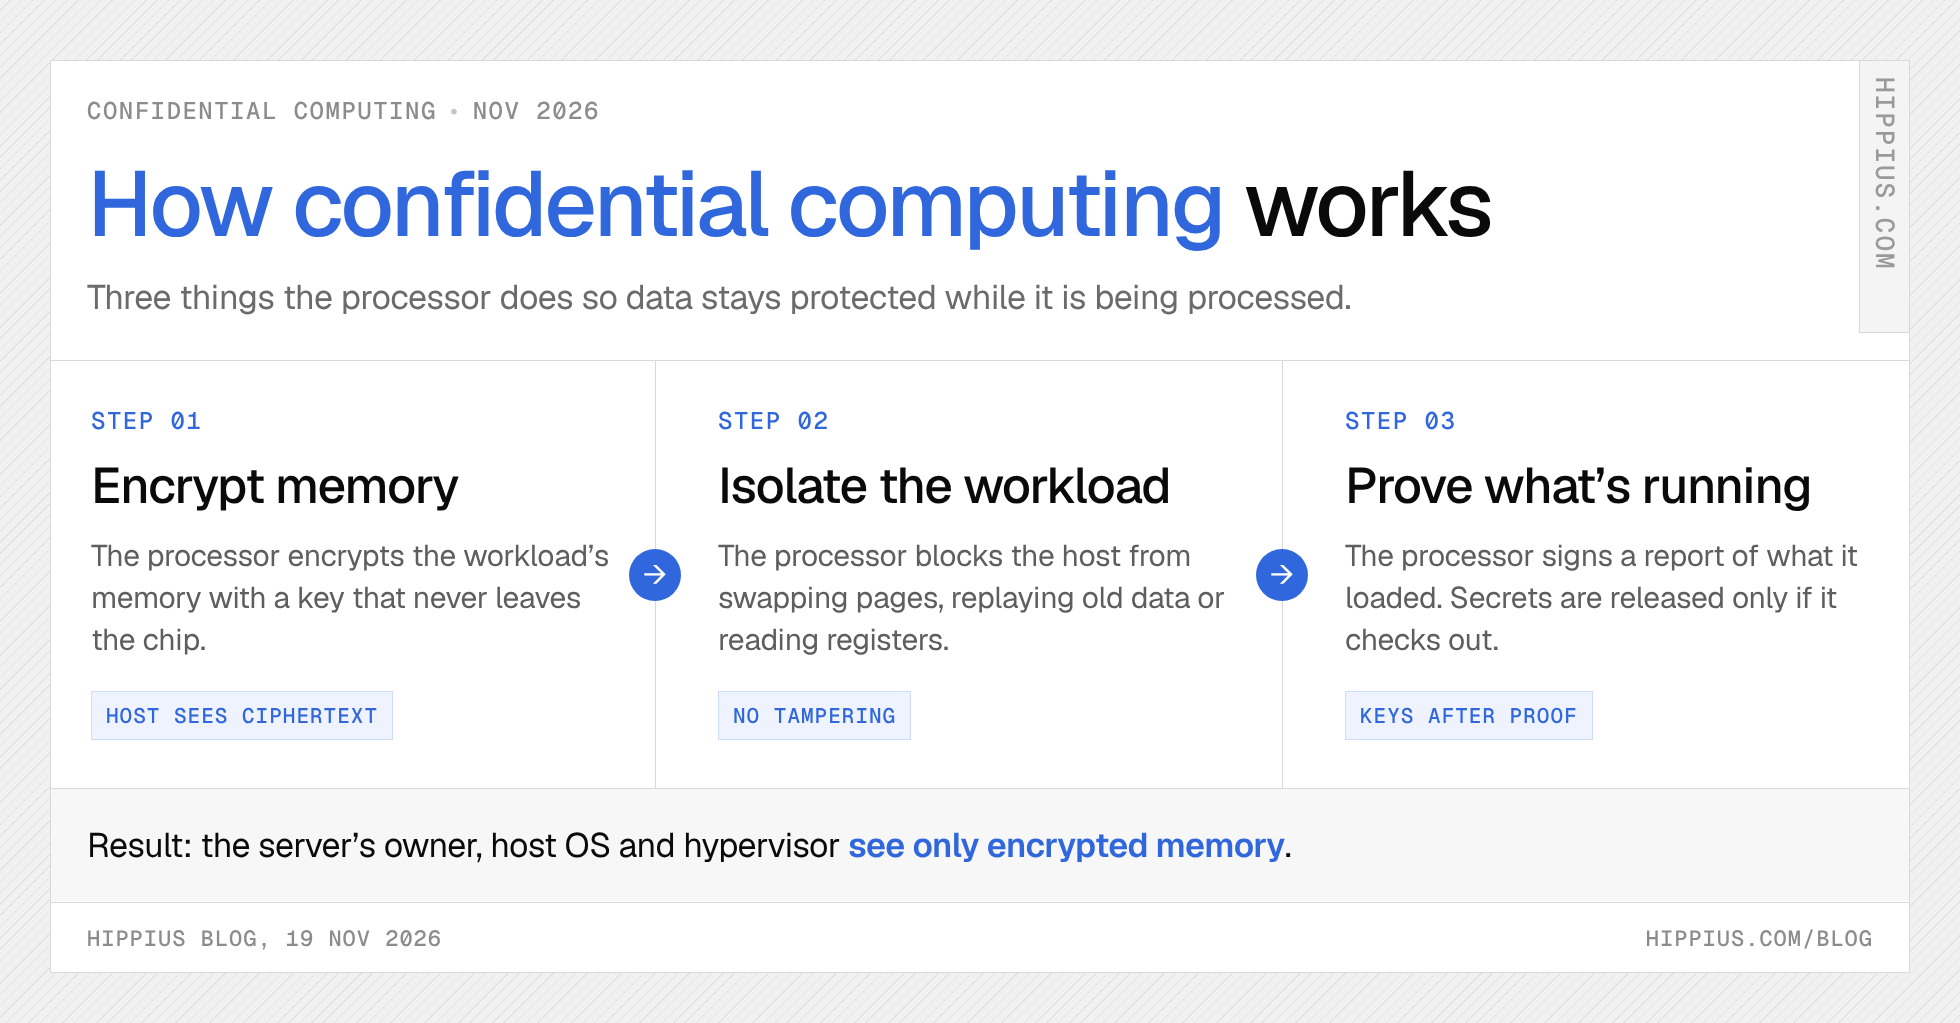
Confidential computing closes that gap with three pieces working together:
- Memory encryption in the processor. The CPU encrypts the workload's memory with a key that never leaves the chip. Code outside the workload, including the hypervisor, sees only ciphertext.
- Isolation. The processor blocks the host from tampering with the workload's memory and CPU state, so it can't swap pages, replay old data or peek at registers.
- Attestation. The processor signs a report of exactly what software it loaded. You, or a service acting for you, check that report before releasing secrets such as a disk key.
Encryption without attestation would be a promise you can't check. Attestation is what lets you check it for yourself.
What is a trusted execution environment?
A trusted execution environment (TEE) is an area of a processor that runs code and holds data in isolation from the rest of the machine, including the operating system and hypervisor, and that can prove what it's running. TEEs come in two shapes.
Secure enclaves protect one part of one application. You split your program so the sensitive part runs inside the enclave and the rest runs outside. Intel SGX is the best-known example. It gives the smallest trust boundary, because even the operating system is outside it, but you have to rewrite software around it.
Confidential VMs protect an entire virtual machine. The processor encrypts the whole VM's memory, and you run an ordinary Linux image inside. The guest operating system is now inside the trust boundary, which makes it larger, but most software runs without changes. AMD SEV-SNP and Intel TDX both work this way, and that ease of use is why the big clouds sell confidential VMs rather than enclaves.
So a secure enclave is one kind of TEE, and a confidential VM is another. Every enclave is a TEE; not every TEE is an enclave.
Enclaves look to be fading on servers. In October 2026 Guru3D reported, citing Tom's Hardware, that Intel plans to drop SGX after its Diamond Rapids Xeon generation and focus on TDX. Intel hasn't confirmed this. Existing SGX systems keep working, but new projects are better off starting on a confidential VM.
How attestation works
When a confidential VM starts, the processor measures what it loads: the firmware, the boot image and its configuration. It puts that measurement in a report and signs it with a key that traces back to AMD or Intel, so nobody, including the server's owner, can forge it.
A verifier then checks two things: that the signature comes from genuine hardware, and that the measurement matches software it expects. If both pass, the verifier releases a secret to the VM, usually the key to its disk. If either fails, the VM gets nothing and can't read its own data.
Hippius Compute is a worked example. Every Hippius VM runs as an AMD SEV-SNP confidential VM, and its disk stays locked until attestation passes:
- The VM boots and sends its signed SEV-SNP report to Hippius's key broker.
- The key broker, which itself runs inside an SEV-SNP VM and must attest to Hippius's key vault, checks the measurement against an allowlist of images that Hippius builds and signs.
- Only if the report passes does the broker encrypt the disk key to that VM. A VM that fails attestation can't unlock its disk.
- The console shows the attestation result and the raw SEV-SNP report, so you can inspect it yourself.
- Deleting a VM crypto-erases it, backups included.
The full walkthrough, including the trust model, is in how Hippius attestation works.
The important question in any attestation flow is who runs the verifier. On Azure, Microsoft Azure Attestation can do it as a managed service, and Google Cloud's Confidential Space uses Google's own attestation service. On AWS and Oracle Cloud you receive the signed report and verify it with your own service. On Hippius, Hippius runs the key broker. Whoever runs the verifier decides which software receives your keys, which is why it appears in the next section.
What each setup hides
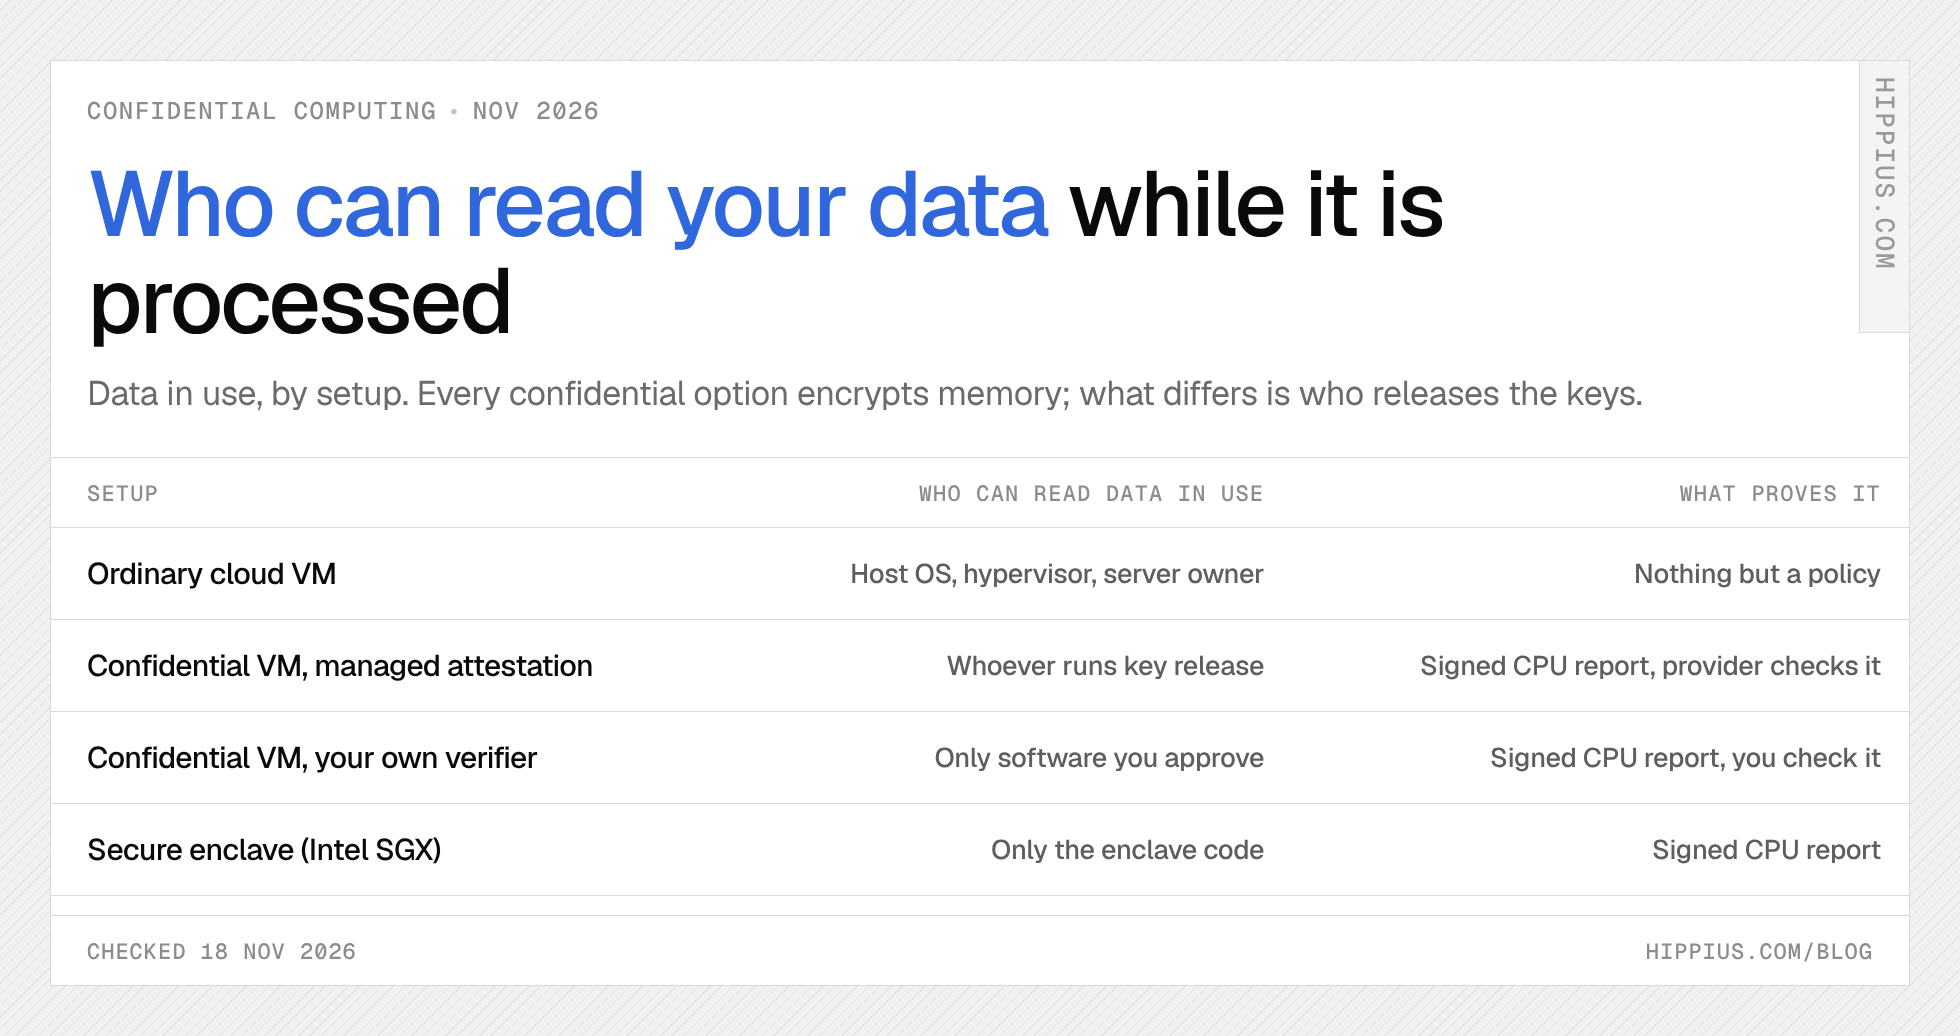
| Setup | Who can read data in use | What proves it | Effort |
|---|---|---|---|
| Ordinary cloud VM | The host OS, hypervisor and server's owner | Nothing but the provider's policy | None |
| Confidential VM, managed attestation | Whoever runs key release, if they approve a malicious image | Signed CPU report, checked by the provider | Pick a confidential VM type |
| Confidential VM, your own verifier | Only software you approve | Signed CPU report, checked by you | Run your own attestation service |
| Secure enclave (Intel SGX) | Only the enclave code | Signed CPU report | Rewrite the sensitive part of your app |
Most teams land on the second row: a confidential VM where the provider handles attestation. It removes the server's owner and the host software from the picture with almost no work. The third row removes the provider too, at the cost of running your own verifier.
AMD SEV-SNP vs Intel TDX
Almost every confidential VM you can rent today runs on one of two technologies.
| AMD SEV-SNP | Intel TDX | |
|---|---|---|
| Processors | AMD EPYC, 3rd generation (7003) and later | Intel Xeon, 4th generation and later in cloud use |
| What it isolates | A whole VM | A whole VM, called a trust domain |
| Memory | Encrypted, with integrity protection against replay and remapping | Encrypted, with CPU state shielded from the host |
| Attestation | Signed report from the AMD Secure Processor | Signed quote via Intel's TDX module |
| Offered by (Nov 2026) | Azure, Google Cloud, AWS, Oracle Cloud, Hippius | Azure, Google Cloud |
AMD's SEV page describes SEV-SNP as adding memory integrity on top of earlier SEV versions, to block hypervisor attacks such as data replay and memory remapping. Intel's TDX page describes trust domains as hardware-isolated VMs whose memory is opaque to the cloud provider.
For a buyer, they do the same job: a whole Linux VM with encrypted memory, no code changes, and a signed report you can check. SEV-SNP is more widely available in November 2026, since every provider in this post offers it and only Azure and Google Cloud offer TDX. Choose by the provider you want to use, unless your security team or your attestation tooling prefers one.
Confidential AI
Confidential AI means running AI work inside a TEE so that prompts, user data and model weights stay encrypted while they're processed. It works in two directions: a company can send private data to a model without the host seeing it, and a model owner can run its weights on someone else's hardware without exposing them.
Training and large-model inference run on GPUs, so they need a confidential GPU, where the GPU joins the TEE and data stays encrypted between processor and GPU. As of 18 November 2026, Azure offers this on its NCCadsH100v5 VMs (NVIDIA H100), and Google Cloud on A3 (H100, Spot and Flex-start only) and G4 (RTX PRO 6000). We didn't find a confidential GPU option on AWS EC2, Oracle Cloud or Hippius.
CPU-only TEEs still cover a lot of the work around AI: agents that hold API keys and user data, pipelines that clean or redact private records before they reach a model, retrieval services, and small models that run on a CPU. If the model itself needs a GPU and the data must stay encrypted, Azure and Google Cloud are the options today for running it yourself.
If you want to call a model rather than host one, private inference gives you the same protection through an API. SayGM, an AI gateway, passes every request through an Intel TDX enclave and runs the open-weight models on its confidential tier inside it end to end; frontier models such as Claude and GPT are relayed through it, but their maker still sees the prompt. SayGM's guide to private inference explains how the processor and GPU are both sealed for AI, and how to check a provider's privacy claim.
What confidential computing doesn't protect
A TEE narrows who can see your data. It doesn't make a workload safe on its own.
- Side channels. Researchers keep finding ways to infer data from the timing, power or cache behaviour of TEEs. Vendors patch them through firmware and microcode, which is one reason attestation reports include firmware versions.
- Your own software. A confidential VM hides memory from the host. Your app inside the VM still sees it, so a vulnerable app, a leaked SSH key or a bad dependency is just as exploitable.
- The key-release service. Whoever runs the verifier decides which software gets your secrets. If that operator is compromised, or approves a malicious image, the TEE will faithfully run it with your keys.
- Availability and metadata. The host can't read your VM, but it can stop it, slow it down, and see that it's running, how busy it is and where its traffic goes.
Hippius's docs apply this to Hippius directly. You trust AMD's processor and firmware, and Hippius for "the images it builds and allowlists, the KBS and key vault that hold your disk key." The docs list a "malicious or compromised Hippius" as outside what the design protects against, noting that it "could run its own code inside your VM." In practice, the server's owner can't read your VM, but Hippius manages key release. Disk keys held by the customer, which would take Hippius out of that path, "are being built and are not available yet."
The big clouds are in a similar position when you use their managed attestation: you're trusting Microsoft or Google to run the verifier honestly. The difference is that on Azure, Google Cloud, AWS and Oracle Cloud you can run your own verifier today.
When confidential computing is worth it
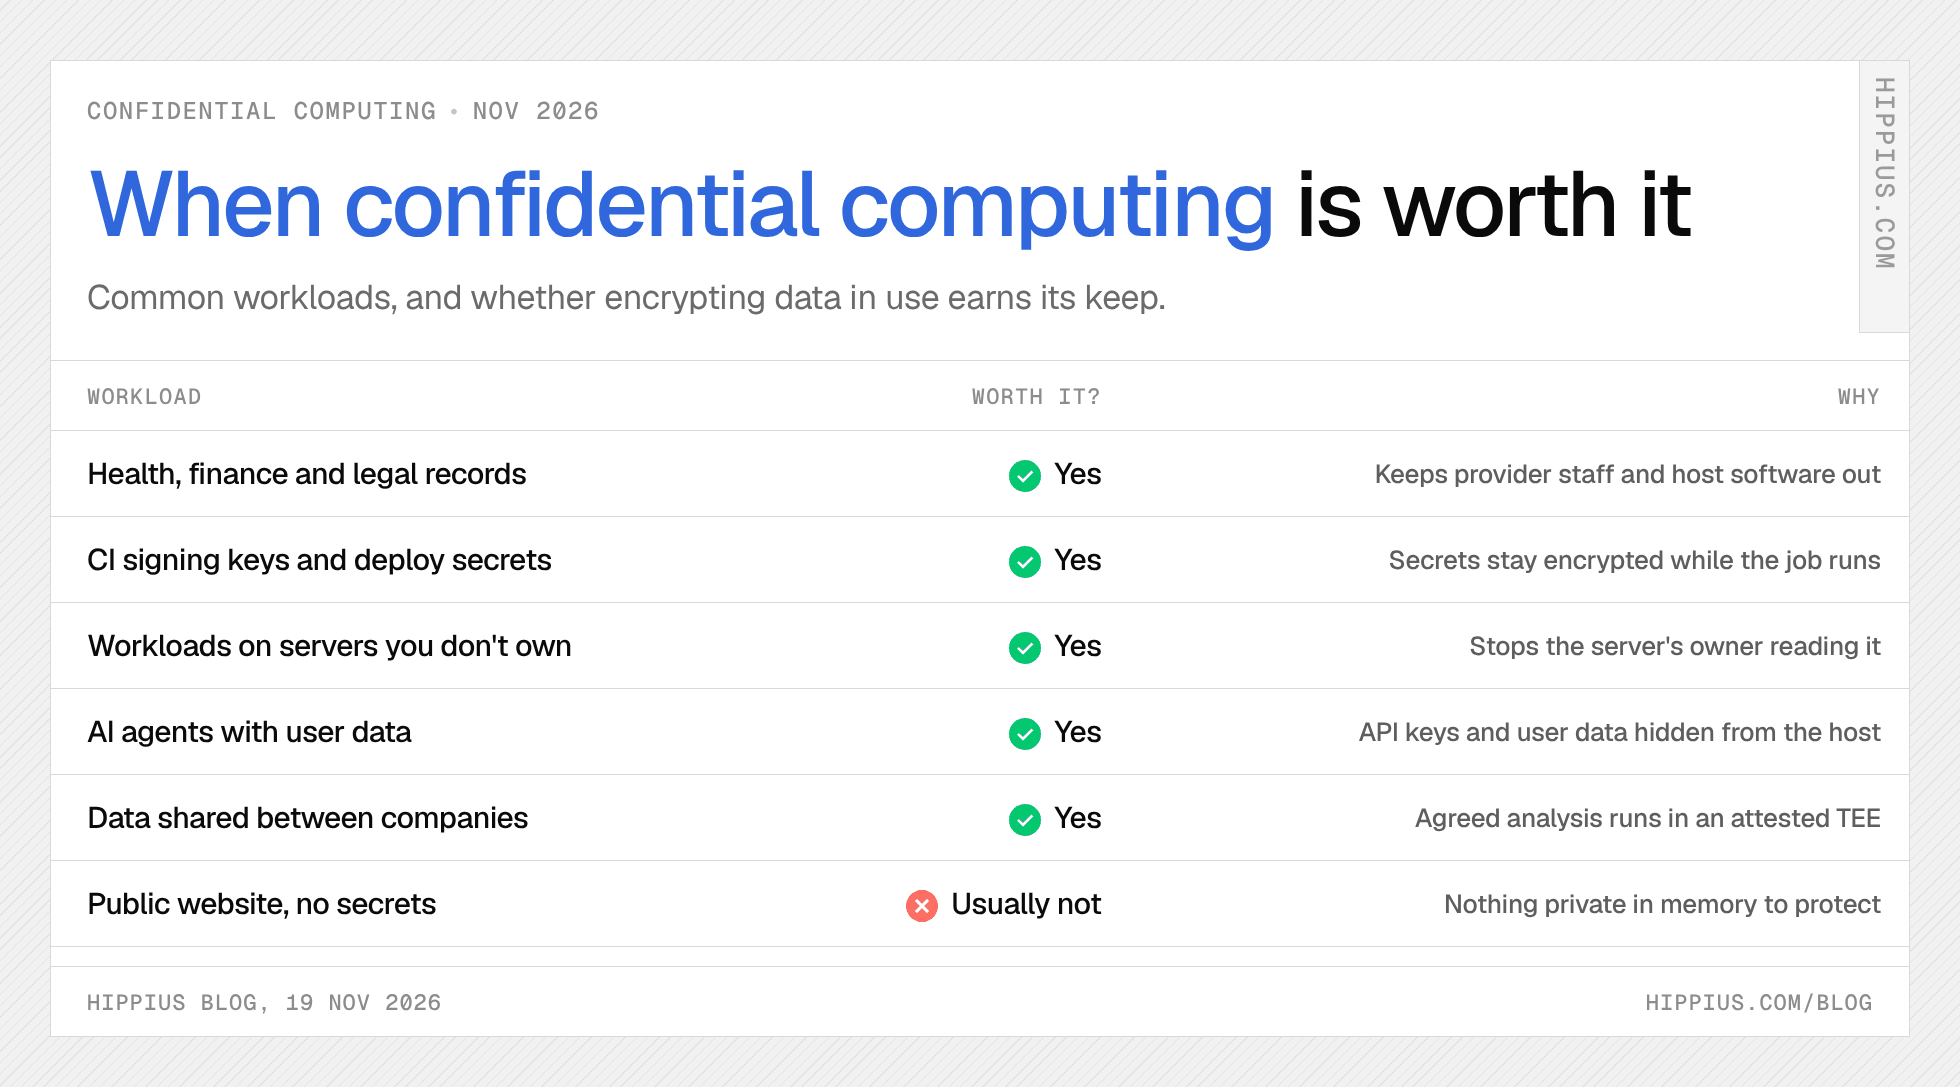
- Regulated or personal data. Health, finance and legal records processed in the cloud, where you want the provider's staff and host software out of the picture.
- Secrets in CI. Build pipelines handle signing keys and deploy credentials. A confidential runner, such as Hippius's single-use GitHub Actions runners, keeps them encrypted while the job runs.
- Hardware you don't own. On third-party or distributed servers, a TEE is what stops the server's owner reading your workload. It's why Hippius runs every VM, database and Kubernetes node as a confidential VM on servers run by independent operators, and why it built a WAF that runs inside confidential VMs for its CDN.
- AI agents with user data. Agents hold API keys and read private data. Running them in a confidential VM keeps both out of the host's view.
- Sharing data between companies. When two parties want to combine data neither should see, an attested TEE can run the agreed analysis. Google Cloud's Confidential Space is built for this.
It's usually not worth it for public websites, stateless services with no secrets, or workloads where you already own and control the hardware.
Cost is rarely the obstacle. On 18 November 2026, AWS charged 10% on top of the normal instance price for SEV-SNP, Google Cloud's SEV-SNP surcharge added about 10% to an n2d-standard-2, and Oracle Cloud charged nothing extra. Hippius has no surcharge because every VM is confidential; see Hippius pricing.
What confidential compute means on Hippius
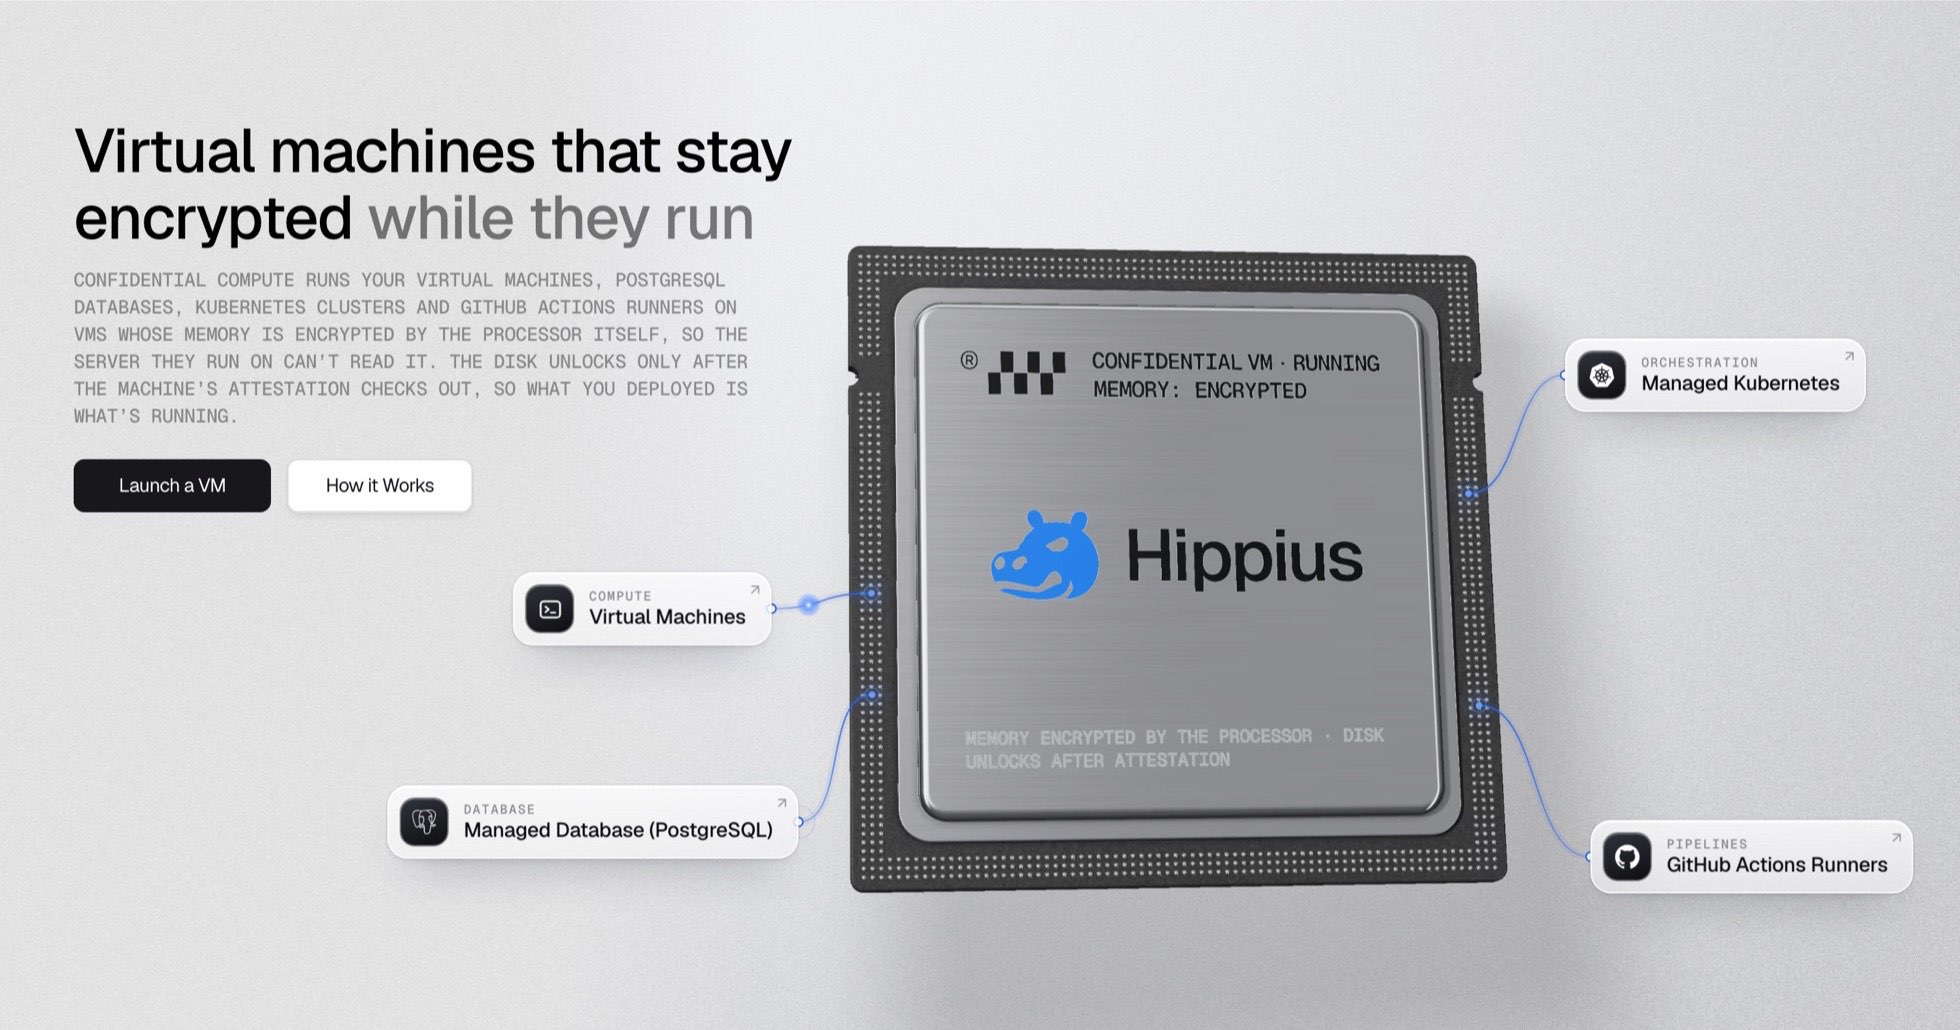
On Hippius, confidential computing isn't an add-on. Hippius Compute runs on servers owned by independent operators rather than in its own data centres, and the TEE is what makes that safe: the operator can run your workload but can't read it. So every VM, managed PostgreSQL instance, Kubernetes node and GitHub Actions runner is an AMD SEV-SNP confidential VM, with no special instance type to choose.
The design goes past the TEE in three ways:
- Secrets only you hold. You give Hippius only the public half of your SSH key, and the browser terminal runs the SSH handshake in your browser, so your private key never reaches Hippius. A database's password, TLS certificates and backup key are shown once, at creation, and can't be shown again or reset. A Kubernetes cluster key is generated in your browser, and Hippius only ever sees its public half.
- Backups stay sealed. VM backups are copies of the encrypted disk, opened only by that VM's disk key. Database and Kubernetes backups are encrypted inside the workload before they're stored, database backups in your own Object Storage bucket.
- Deleting means gone. Deleting a VM crypto-erases it: its key is destroyed, so its disk and every backup can no longer be decrypted.
The limit is the one covered above: Hippius manages disk-key release until customer-held keys arrive.
Which providers offer confidential computing
| Provider | TEE technology | Confidential VMs | Confidential GPUs | Containers and Kubernetes | Attestation |
|---|---|---|---|---|---|
| Microsoft Azure | AMD SEV-SNP, Intel TDX | DCasv5, ECasv5 and v6 (SEV-SNP); DCesv6, ECesv6 (TDX) | NCCadsH100v5 (H100) | AKS confidential node pools | Managed (Azure Attestation) or your own |
| Google Cloud | AMD SEV, SEV-SNP, Intel TDX | N2D, C2D, C3D, C4D (SEV); N2D (SEV-SNP); C3 (TDX) | A3 (H100), G4 (RTX PRO 6000) | Confidential GKE nodes | Managed for Confidential Space, or your own |
| AWS | AMD SEV-SNP | m6a, c6a, r6a in Ohio and Ireland | Not found | Not found | Your own |
| Oracle Cloud | AMD SEV-SNP, SEV | E5, E6 (SEV-SNP); E3, E4 (SEV) | Not found | Not found | Your own |
| Hippius | AMD SEV-SNP | Every VM | None | Managed Kubernetes, all nodes confidential | Managed, shown in the console |
Checked 18 November 2026 against each provider's own documentation.
Microsoft Azure has the widest range. You can choose between AMD SEV-SNP and Intel TDX, run confidential VM node pools in AKS, use H100 GPUs inside the TEE, and hand attestation to Microsoft Azure Attestation. It's the natural choice for teams already on Azure, and the first stop for confidential AI on GPUs.
Google Cloud treats confidential computing as an option you switch on for supported machine types, with a surcharge on top. It covers SEV, SEV-SNP and TDX, offers confidential GKE nodes and confidential GPUs, and has Confidential Space for multi-party data sharing, which no other provider here matches.
AWS offers AMD SEV-SNP on a few instance families in two regions, US East (Ohio) and Europe (Ireland), and you verify the attestation report yourself. Its other isolation product, Nitro Enclaves, carves a separate environment out of an EC2 instance using the Nitro system rather than a CPU TEE, and it can't be combined with SEV-SNP on the same instance.
Oracle Cloud supports SEV-SNP on its E5 and E6 shapes and the older SEV on E3 and E4, at no extra cost, with bring-your-own attestation.
Hippius makes every workload confidential by default instead of selling a special instance type. Linux VMs, managed PostgreSQL, managed Kubernetes and GitHub Actions runners all run as AMD SEV-SNP confidential VMs, on servers run by independent operators, billed per second from a balance with no contract. The limits: AMD only, no GPUs, a choice of countries limited to where verified servers have room, and Hippius manages key release until customer-held keys arrive. The Hippius Compute docs cover setup, and the launch post introduces Hippius confidential VMs.
Common questions about confidential computing
What is confidential computing?
Confidential computing keeps data encrypted while it is being processed, by running the workload inside a hardware trusted execution environment that the server's owner, host operating system and hypervisor can't read. A signed attestation report proves the environment is genuine. As of November 2026, Azure, Google Cloud, AWS, Oracle Cloud and Hippius all offer it as confidential VMs.
What is a trusted execution environment (TEE)?
A TEE is an isolated area of a processor that runs code and holds data out of reach of the rest of the machine, and can prove what it's running through attestation. The common server TEEs in 2026 are AMD SEV-SNP and Intel TDX, which protect a whole virtual machine.
Is a secure enclave the same as a TEE?
A secure enclave is one kind of TEE that protects part of an application, such as Intel SGX. A confidential VM is another kind that protects a whole virtual machine. Every enclave is a TEE, but not every TEE is an enclave.
What is attestation in confidential computing?
Attestation is a report, signed by the processor, of exactly what software a TEE loaded. A verifier checks the signature and the measurement, and only then releases secrets such as a disk key. On Hippius, a VM that fails attestation can't unlock its own disk.
What is the difference between AMD SEV-SNP and Intel TDX?
Both encrypt a whole VM's memory, produce a signed attestation report and run ordinary Linux without code changes. SEV-SNP runs on AMD EPYC processors and adds memory integrity protection; TDX runs on Intel Xeon processors. In November 2026, SEV-SNP is offered by Azure, Google Cloud, AWS, Oracle Cloud and Hippius, and TDX by Azure and Google Cloud.
Which cloud providers offer confidential VMs?
As of 18 November 2026: Microsoft Azure (AMD SEV-SNP and Intel TDX), Google Cloud (AMD SEV, SEV-SNP and Intel TDX), AWS (AMD SEV-SNP in Ohio and Ireland), Oracle Cloud (AMD SEV-SNP and SEV), and Hippius (AMD SEV-SNP on every VM, database, Kubernetes node and CI runner).
How much does a confidential VM cost?
Usually little more than a normal VM. On 18 November 2026, AWS added 10% to the instance price for SEV-SNP, Google Cloud's surcharge added about 10% to an n2d-standard-2, Oracle Cloud charged nothing extra, and Hippius has no surcharge because every VM is confidential.
What is confidential AI?
Confidential AI is running AI work inside a TEE so prompts, user data and model weights stay encrypted while they're processed. GPU workloads need a confidential GPU, which Azure (H100) and Google Cloud (H100 and RTX PRO 6000) offer as of November 2026; CPU TEEs cover agents, data pipelines and small models.
Can the cloud provider see my data in a confidential VM?
Not by reading memory: the processor keeps it encrypted from the host, hypervisor and server's owner. But whoever runs key release decides which software gets your keys. On Hippius, the server's owner can't read your VM, but Hippius manages key release, and customer-held keys aren't available yet.
About Hippius
Hippius is a distributed cloud platform built to give users a verifiable alternative to providers like AWS and Google Cloud. Files are encrypted and distributed across an independent network rather than held in a single provider's data center. Every storage claim, payment, and miner action is recorded on Hippius's own blockchain, so instead of asking users to trust the platform, Hippius lets them check it for themselves. On top of that foundation sits a full product suite: personal cloud storage, S3-compatible object storage with no egress fees, a CDN that serves stored files from the edge, confidential computing on secure hardware, and a container and model registry for AI.
Website | Discord | Twitter | Docs | Blog | Medium | Forum | Github | LinkedIn